Explore capacity building resources developed through CURIUM to support SMEs, organisations and professionals in understanding and navigating European cybersecurity and digital regulatory requirements.
The resources cover the Cyber Resilience Act (CRA), cybersecurity compliance, the interplay between the CRA and the AI Act, conformity assessment and practical approaches to strengthening cyber resilience.
Getting to Know the Cyber Resilience Act (CRA)
An introduction to the EU Cyber Resilience Act (CRA) and its implications for products with digital elements. The material covers the scope of the CRA, essential cybersecurity requirements, economic operators and key obligations for organisations preparing for compliance.
Cyber Resilience Act: Overview of Articles 1–34
An overview of the CRA’s scope, key definitions, product categories, obligations for manufacturers and other economic operators, and conformity assessment and CE marking.
Cyber Resilience Act: Overview of Articles 35–71
An overview of the authorities involved in CRA implementation and the procedures for market surveillance, addressing product risks and handling non-compliance.
An SME’s Guide to Cybersecurity Compliance: The CSA and CRA
A practical guide for SMEs exploring the European cybersecurity compliance landscape, with a focus on the Cybersecurity Act (CSA) and Cyber Resilience Act (CRA). The presentation introduces European cybersecurity certification, CRA requirements, products with digital elements, conformity assessment and manufacturers’ compliance responsibilities.
Cyber Resilience Act (CRA) Compliance and Awareness
A practical training resource designed to strengthen understanding of the Cyber Resilience Act and its application. Through scenario-based training and assessment activities, users explore CRA scope, cybersecurity obligations, vulnerability management, incident reporting and compliance requirements.
Interplay between the AI Act and the Cyber Resilience Act
An exploration of the relationship between the EU AI Act and the Cyber Resilience Act, focusing on areas where cybersecurity and conformity requirements overlap. The presentation examines high-risk AI systems that also qualify as products with digital elements and how CRA cybersecurity requirements interact with the AI Act.
Conformity Assessment for High-Risk AI Systems: The Role of Testing
A focused resource examining conformity assessment for high-risk AI systems under the EU AI Act and the role of testing in demonstrating compliance. It covers conformity assessment activities and bodies, internal and third-party assessment, quality management systems, technical documentation and testing requirements.
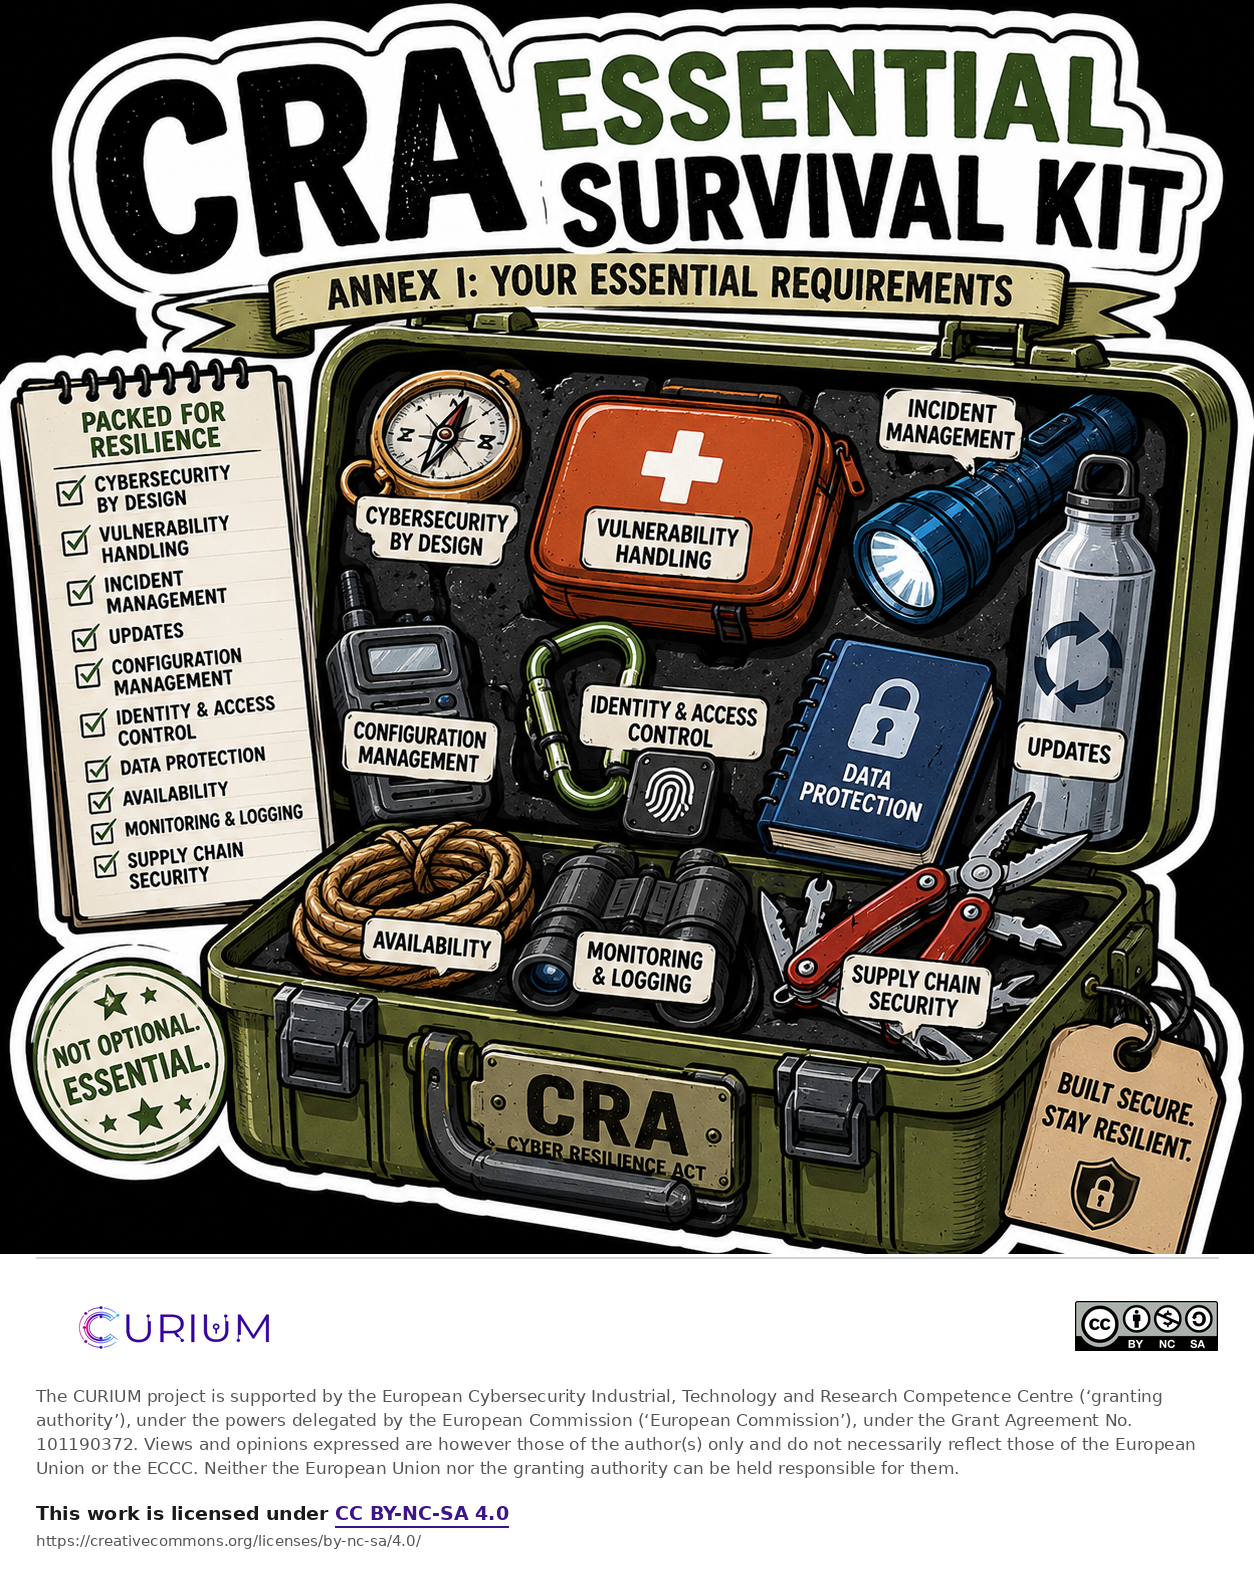
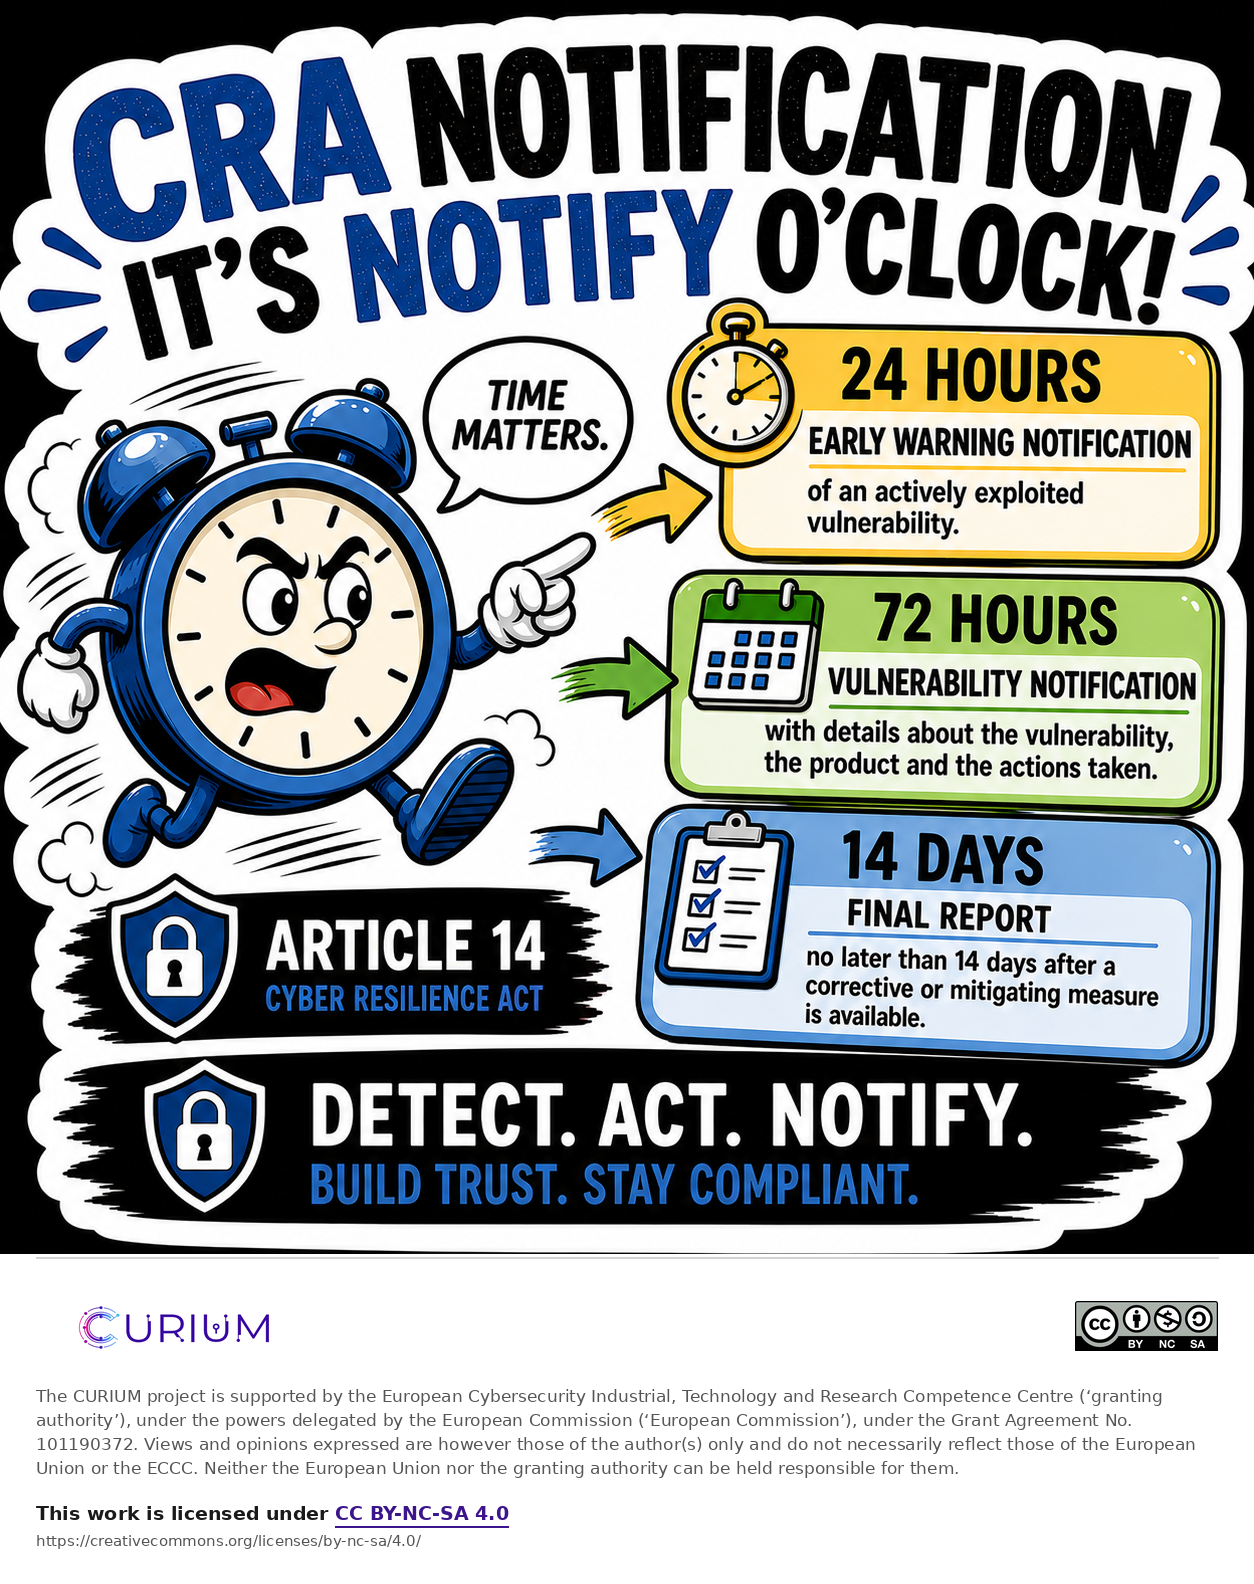
Cybersecurity Awareness Stickers
Explore CURIUM’s illustrated stickers on the Cyber Resilience Act and everyday cybersecurity practices. Click on any sticker to view it in full size or download it.